Healthcare facilities manage some of the most sensitive information about individuals.
Patient demographics, medical histories, diagnoses, laboratory results, prescriptions, insurance information, billing records, and other health information all require careful handling.
As hospitals move from paper records to digital systems, data security becomes an essential part of HMIS implementation.
Kenya's Digital Health Act specifically provides for privacy, confidentiality and security of health data, while the country's digital-health framework also addresses secure transfer of identifiable health information.
Why Patient Data Requires Special Attention
Health information can be highly sensitive.
Unauthorized access can expose information that patients reasonably expect healthcare providers to keep confidential.
For this reason, security should not be considered only an IT department responsibility.
It should be part of the hospital's overall operational processes.
1. Role-Based Access
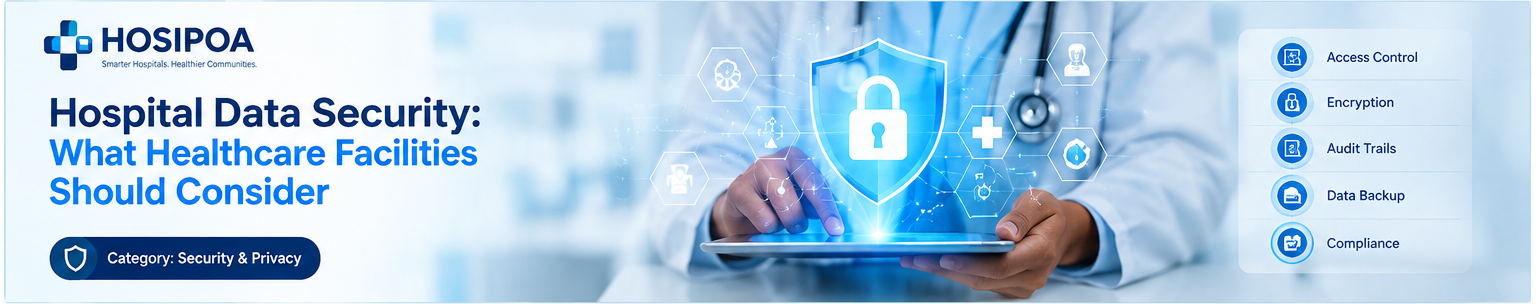
One of the most important principles is ensuring that users only have access to information and functions relevant to their responsibilities.
A receptionist does not necessarily require the same access as a doctor.
A pharmacist has different responsibilities from a laboratory technician.
An administrator may require broader system-management access.
Role-based access allows hospitals to organize permissions around these responsibilities.
2. Strong Authentication
User accounts should be protected using appropriate authentication controls.
Hospitals should consider:
- Strong passwords
- Account management
- Session controls
- Multi-factor authentication where appropriate
- Secure password recovery
- User deactivation when staff leave
The exact controls should reflect the facility's risk profile and technology environment.
3. Audit Trails
A hospital should be able to understand important activity within its information system.
Audit trails can help answer questions such as:
- Who accessed a record?
- When was information changed?
- Which user performed an action?
- What happened to a particular transaction?
This can support accountability and investigation when necessary.
4. Backups and Recovery
Security is not only about preventing unauthorized access.
Hospitals also need to think about availability.
What happens if:
- A server fails?
- Data is accidentally deleted?
- A system becomes unavailable?
- Hardware is damaged?
- A cyber incident affects the system?
Reliable backup and recovery procedures are therefore important components of a healthcare technology strategy.
5. Secure Data Sharing
Modern healthcare increasingly requires information to move between systems.
Kenya's Digital Health Act provides a framework for safe and secure transfer of personal identifiable health data and medical records.
The Office of the Data Protection Commissioner also provides guidance specifically addressing situations where a hospital engages an HMIS provider to manage and analyze patient health records.
This means hospitals should consider not only how data is stored but also how it is shared.
6. Staff Awareness Matters
Technology alone cannot guarantee security.
Staff should understand basic security practices such as:
- Never sharing passwords
- Locking unattended workstations
- Avoiding unauthorized devices
- Recognizing suspicious messages
- Reporting security incidents
- Following access-control policies
A secure HMIS needs secure processes around it.
Building Security Into Hospital Digitization
When choosing or implementing an HMIS, security should be considered from the beginning.
Hospitals should ask vendors about:
- Access controls
- Encryption
- Backups
- Audit trails
- User management
- Data hosting
- Disaster recovery
- Security monitoring
- Data-processing responsibilities
- Incident response
HOSIPOA's Approach
HOSIPOA is built around the idea that hospital software should provide users with access appropriate to their responsibilities.
Role-based access can help facilities create more focused user environments while supporting controlled access to hospital information.
Ultimately, protecting patient information requires a combination of technology, policies, people, and responsible data management.
A modern HMIS should therefore be evaluated not only by what it can do, but also by how responsibly it handles the information entrusted to it.